The quiet endpoints that move your real data.
Your web app, your mobile app, your APIs and your half of the cloud shared-responsibility model. Tested for business-logic flaws, not just the ones a scanner finds.
Which of your endpoints would an attacker reach first?
Every engagement in Software, Cloud & Apps is built to answer that with evidence: reproducible findings, ranked by what they would actually cost you.
4 assessments in this group
Book one on its own, or combine them for end-to-end assurance across the stack.
Web Application Testing
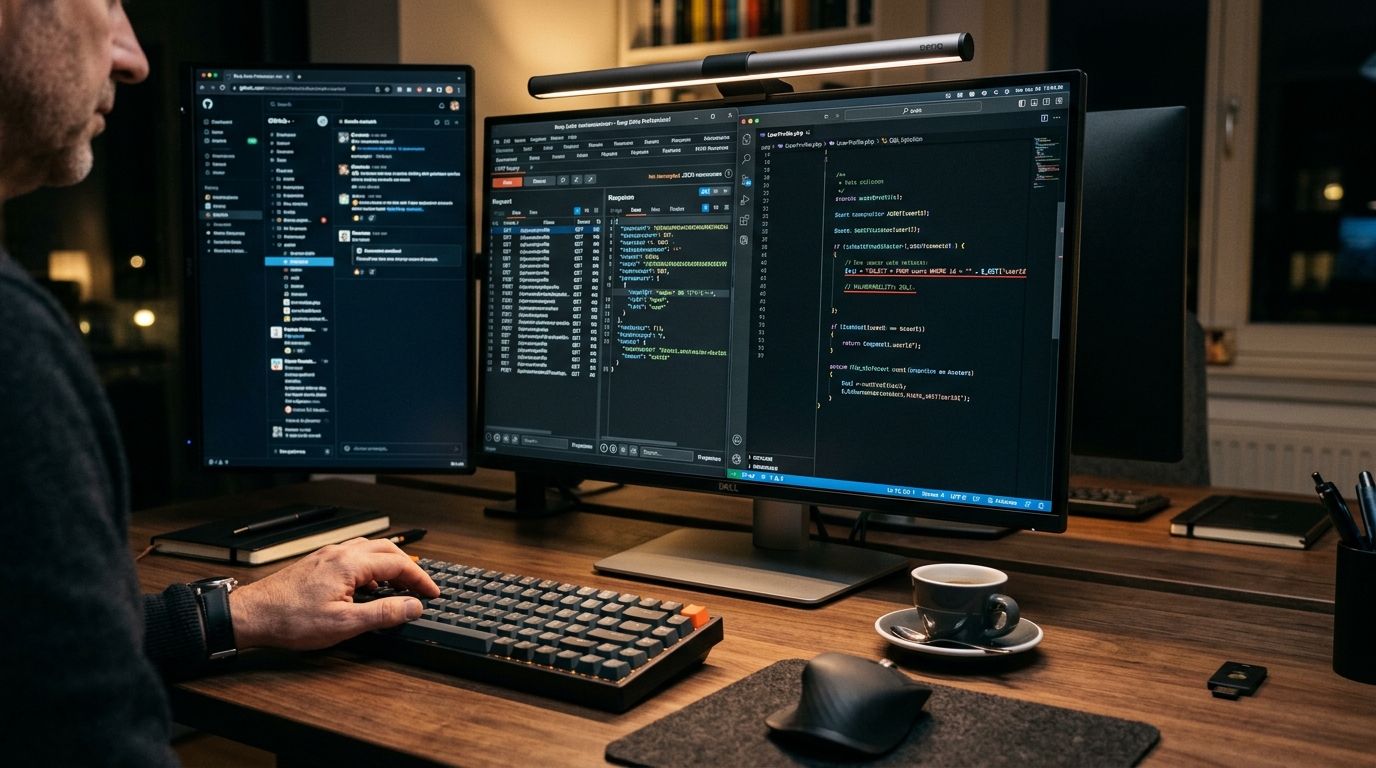
We test your web application the way an attacker uses it, uncovering the subtle business logic flaws scanners consistently miss.
You get: Real, reproducible findings with the exact steps to trigger them, ranked by what they would actually cost you.
Explore assessment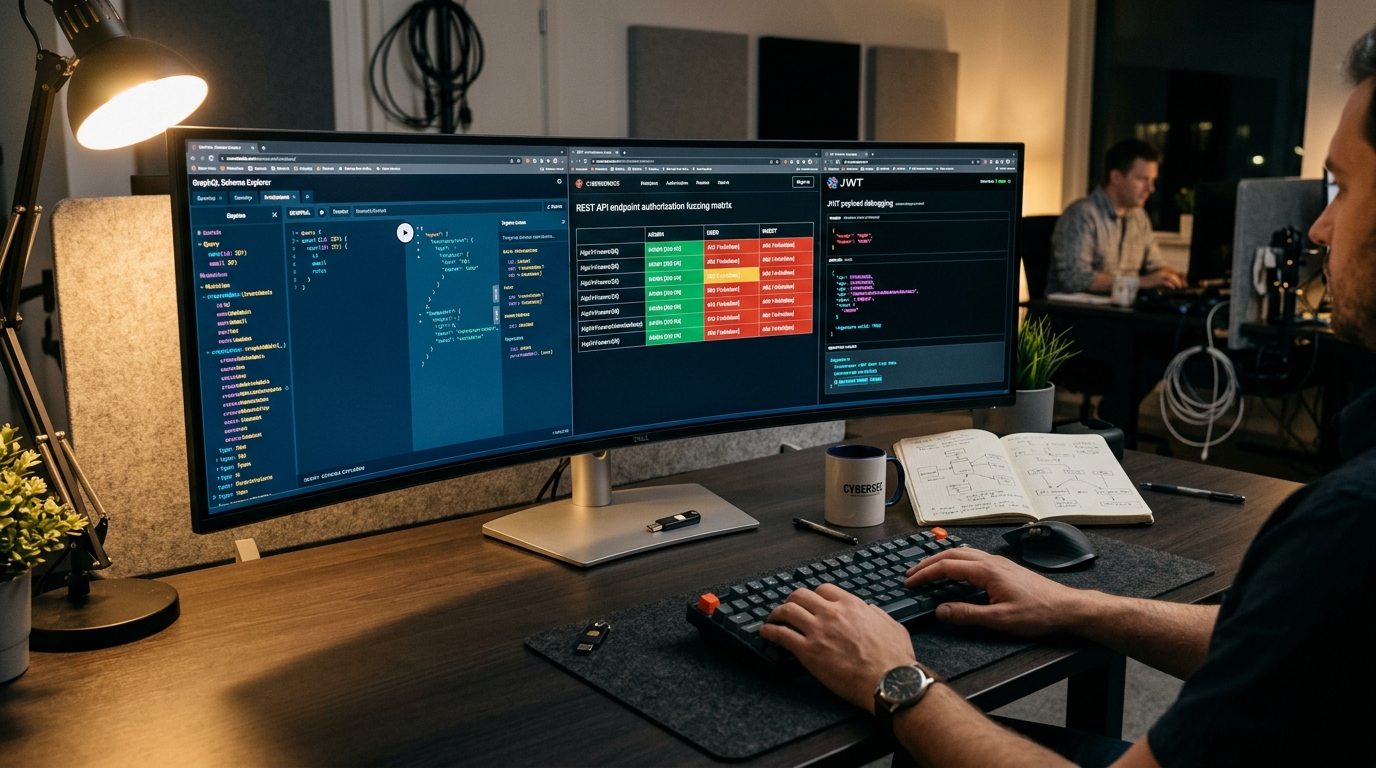
API Security Testing
We go after the endpoints that quietly move your real data, including the ones missing from your documentation.
You get: A map of what your APIs actually expose, and which calls let someone reach data that is not theirs.
Explore assessment
Mobile Application Testing
We test your iOS and Android apps and the backends they talk to, including what the app leaves behind on a lost phone.
You get: App-store-ready findings covering the client, the transport and the server side together.
Explore assessment
Cloud Security Testing
We stress-test your half of the cloud shared-responsibility model, auditing identity, permissions, configuration and gaps between services.
You get: The specific misconfigurations that would let an attacker move sideways through your account, with fixes.
Explore assessmentWhat the work covers
A sample of what each assessment goes after. The full list is on each assessment’s page.
Vulnerability Assessment
Comprehensive scanning using automated tools and manual techniques to identify security weaknesses, misconfigurations, and potential entry points in your web applications.
Penetration Testing
Simulated cyber attacks to test your web application defenses and identify real-world vulnerabilities that could be exploited by malicious actors.
REST API Testing
Comprehensive testing of RESTful APIs including endpoint security, HTTP method validation, parameter manipulation, and response analysis for vulnerabilities.
GraphQL Security
Advanced testing of GraphQL APIs including query depth analysis, schema introspection, authorization bypasses, and mutation vulnerabilities.
Static Analysis
Comprehensive code analysis to identify security vulnerabilities, hardcoded secrets, insecure coding practices, and potential backdoors in mobile application source code.
Dynamic Analysis
Runtime testing of mobile applications to identify security weaknesses, data leakage, and behavioral vulnerabilities during actual application execution.
Cloud Infrastructure Testing
Comprehensive testing of cloud infrastructure including virtual machines, networks, storage, and security configurations across AWS, Azure, and GCP.
Container & Kubernetes Security
Advanced testing of containerized applications, Docker images, Kubernetes clusters, and orchestration platforms for runtime and configuration vulnerabilities.
Ready to scope software, cloud & apps?
Tell us what you are building, when it ships and which deadline you are working to. We will outline the test plan, timeline and deliverables.