A lab, not a checklist factory.

Dellon is a research-led offensive security company. We were founded in 2019 in Pune on a simple, slightly inconvenient belief: the only way to know a product is secure is to genuinely try to break it, applying the tools, time and stubbornness of a real attacker.

The lab

Founded in 2019. Still in the hardware.

Dellon started in Pune in 2019 as a research-led offensive security lab. The belief has not changed: the only way to know a product is secure is to genuinely try to break it, applying the tools, time and stubbornness of a real attacker. We have spent every engagement since earning that.
2019
Founded in Pune, India
30+
Global Security Talks
13
Specialized Offensive Domains
100%
Reproducible Exploits

How we work

Research first. Always has been.

01 / TENET

Hardware-deep

We don't stop at the network layer. From fault injection and side-channels to firmware reverse engineering and RF, we go down to the silicon when that is where the answer lives.

02 / TENET

Standards-aligned

ISO/SAE 21434, UN R155/R156, WP.29, SAE J3061. We speak the language your assessors and OEMs speak, for both AUTOSAR and non-AUTOSAR architectures.

03 / TENET

Evidence over adjectives

Every finding is reproduced and rated. No "critical" without a CAL, a risk value and a way to reproduce it. Your engineers shouldn't have to take our word for anything.

04 / TENET

We give it back

Working groups, bootcamps, conference talks, open research. The field gets better when knowledge is shared rather than hoarded, so we contribute back.

Methodology

How we assess systems.

From bare silicon to integrated cloud telemetry, our workflow is built on rigorous offensive validation.
01

Physical Teardown

Non-destructive and destructive hardware analysis, board imaging, pinout identification, and test-point probing.

02

Bus & Protocol Fuzzing

CAN, LIN, FlexRay, BLE, RF, SPI, UART, and I2C signal inspection with custom hardware glitchers.

03

Firmware Reverse Engineering

Memory dumping, crypto key extraction, bootloader bypasses, and binary vulnerability discovery.

04

CAL-Rated Remediation

Reproducible proof-of-concept exploits, risk rating, and actionable architecture hardening guidance.

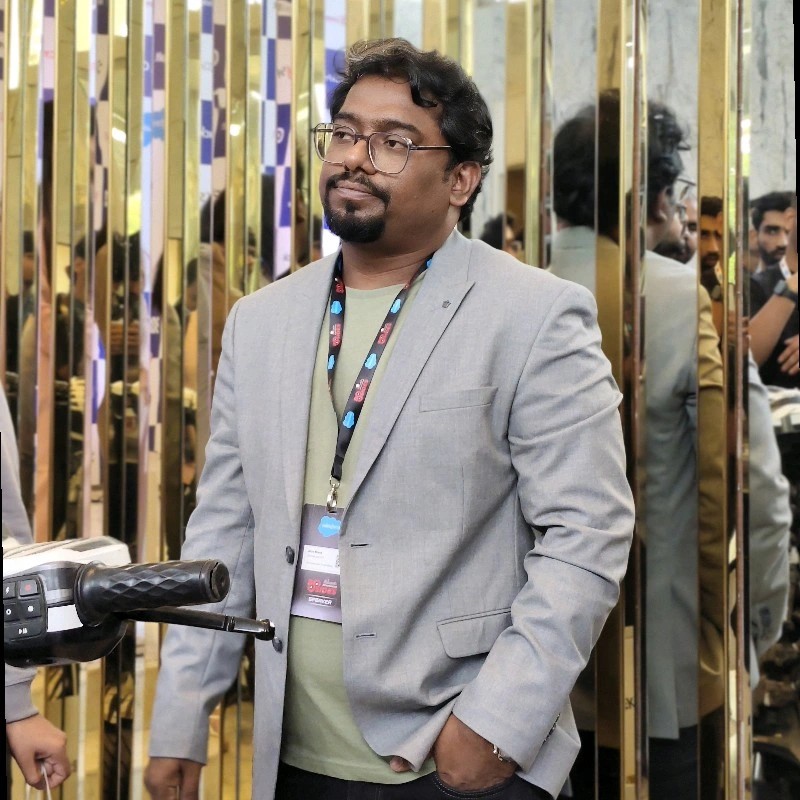
Arun Mane, Founder & CEO

The founder

Arun Mane

Founder & CEO

Hardware hacker by temperament, founder by accident. Arun has spent over a decade pulling apart ECUs, SCADA gear and RF protocols, specializing in fault injection and firmware reverse engineering. He founded the lab in 2019 and co-founded the UnoAcademy training program.

Hardware SecurityAutomotive & SCADAFault InjectionRF ProtocolsFirmware Reverse-Engineering

Arun and the team have presented research at 30 different conferences across 8 countries since 2017.

Frequently Asked Questions

Questions & Answers

Everything you need to know about our offensive research methodology, hardware testbenches, and assessment delivery.

Security testing evaluates systems, hardware, and firmware to identify critical vulnerabilities before malicious actors can exploit them. It protects IP, prevents catastrophic operational breaches, safeguards user safety, and ensures compliance with strict international automotive (ISO/SAE 21434, UN R155) and industrial cybersecurity standards.

We provide deep offensive security assessments across 13 specialized domains, including physical hardware teardowns, automotive ECU and CAN bus fuzzing, firmware reverse engineering, ICS/SCADA infrastructure testing, medical device (IoMT) evaluations, cloud/API security, and custom adversary simulations.

Traditional QA verifies whether a system performs its expected functionality under normal conditions. Security testing operates from a malicious attacker's mindset, deliberately probing edge cases, side-channels, fault injection vulnerabilities, and unintended states to break assumptions and expose silicon-level weaknesses.

We specialize in mission-critical environments: automotive OEMs and Tier-1 suppliers, electric vehicle mobility, industrial automation & SCADA power grids, smart connected IoT devices, aerospace & satellite comms, healthcare medical equipment, and enterprise cloud systems.

Security testing is most effective when integrated throughout the engineering lifecycle, including during board prototyping, firmware revisions, and prior to final type approvals or production deployment. Regular periodic assessments are essential as threat landscapes and exploitation tools evolve.

Yes. We support early-stage hardware startups validating their initial PCBs, high-growth scale-ups, and multinational Tier-1 automotive and industrial conglomerates with turnkey proof-of-concept testing, threat modeling, and CAL-rated executive reporting.

Let’s find it before someone else does.

Tell us what you are building and when it ships. We will tell you honestly whether we are the right team for it, and what an assessment would involve.

Usually a reply within one business day · Mon–Sat · 10:00–18:00 IST