Web Application Testing.
We test your web application the way an attacker uses it, uncovering the subtle business logic flaws scanners consistently miss.
The attack surface & hardware challenge
Offensive reverse-engineering down to the physical silicon, flash extraction, and protocol buses to uncover deep architectural flaws.
The Web Application Security Challenge
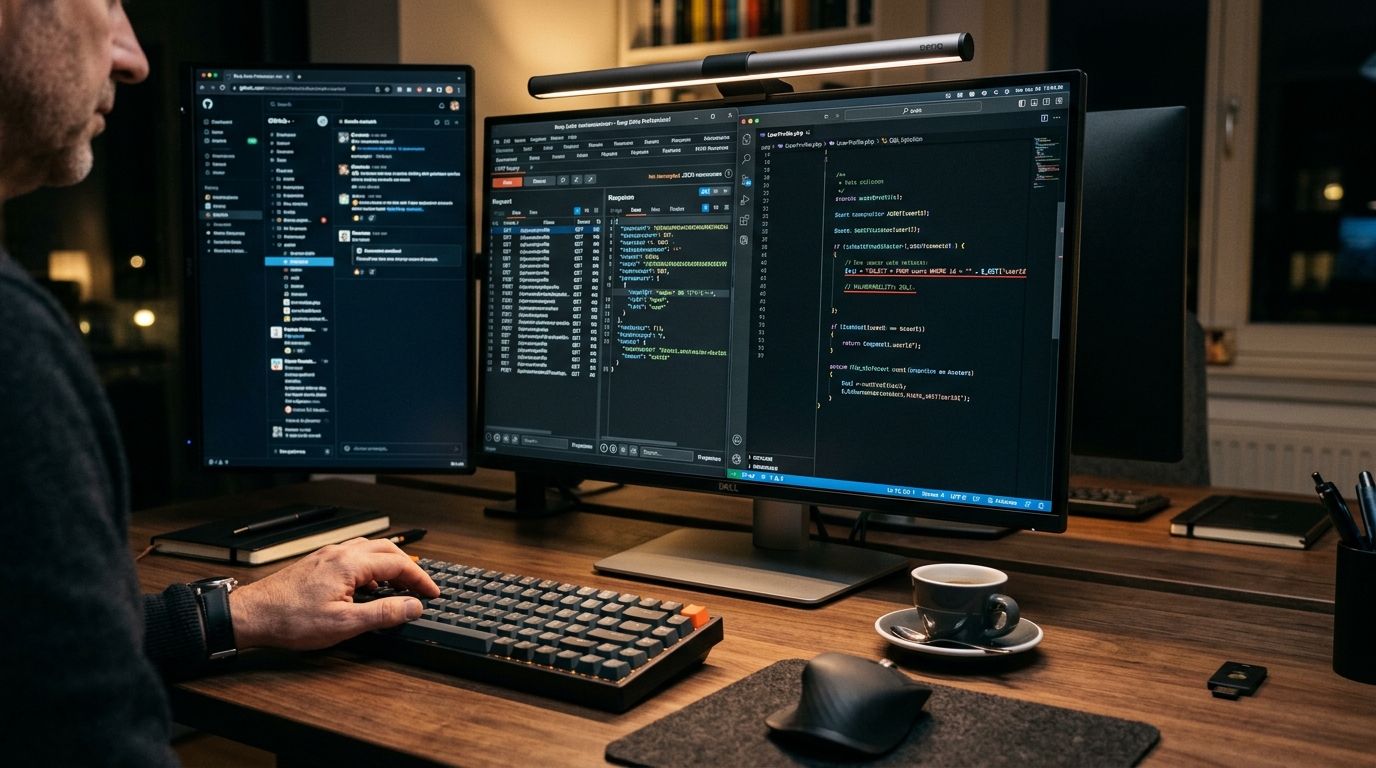
Web applications are the backbone of modern business operations, handling sensitive data, processing transactions, and providing critical services to users worldwide. As web technologies become increasingly sophisticated, so do the attack vectors that threaten them. At Dellon, we understand that web application security extends beyond finding isolated bugs to protect your digital presence, customer data, and business reputation.
What the assessment covers
Exhaustive penetration testing vectors executed across hardware, firmware, interface buses, and logic layers.
Vulnerability Assessment
Comprehensive scanning using automated tools and manual techniques to identify security weaknesses, misconfigurations, and potential entry points in your web applications.
Penetration Testing
Simulated cyber attacks to test your web application defenses and identify real-world vulnerabilities that could be exploited by malicious actors.
Authentication & Authorization
Testing user authentication mechanisms, session management, role-based access controls, and privilege escalation vulnerabilities.
API Security Testing
Comprehensive testing of REST APIs, GraphQL endpoints, and web services for injection attacks, authentication bypasses, and data exposure.
How we run the engagement
Structured four-phase offensive methodology engineered to minimize engineering friction and deliver clear, actionable findings.
Reconnaissance & Mapping
Comprehensive analysis of your web application architecture, technology stack, and attack surface to identify potential entry points and security boundaries.
Vulnerability Discovery
Systematic testing using automated scanners, manual testing techniques, and custom exploit development to identify security weaknesses across all application layers.
Exploitation & Validation
Controlled exploitation of identified vulnerabilities to demonstrate real-world impact, assess risk levels, and validate security control effectiveness.
Reporting & Remediation
Detailed findings report with step-by-step exploitation details, risk assessment, and prioritized remediation recommendations for immediate implementation.
Why engineering teams choose this assessment
Evidence-based vulnerability research designed to unblock compliance, protect launch timelines, and prevent post-shipment recalls.
Web Technology Expertise
Deep understanding of modern web frameworks, JavaScript frameworks, cloud platforms, and emerging web technologies across various industries.
Comprehensive Testing
Holistic approach covering front-end security, back-end vulnerabilities, API security, database security, and infrastructure configurations for complete coverage.
Practical Solutions
Actionable recommendations for real-world security improvements that can be implemented immediately with clear code examples and remediation guidance.
Proven Track Record
Successfully tested 300+ web applications and identified 200+ critical vulnerabilities across e-commerce, banking, SaaS, and enterprise platforms.
Cutting-Edge Tools
Advanced vulnerability scanners, custom exploitation frameworks, and proprietary methodologies for identifying complex vulnerabilities in modern web applications.
24/7 Support
Round-the-clock security consultation and emergency response for critical web application security incidents. We're always available when your web security matters most.
Also in Software, Cloud & Apps
Teams booking Web Application Testing frequently combine it with these adjacent assessments for end-to-end assurance.
API Security Testing
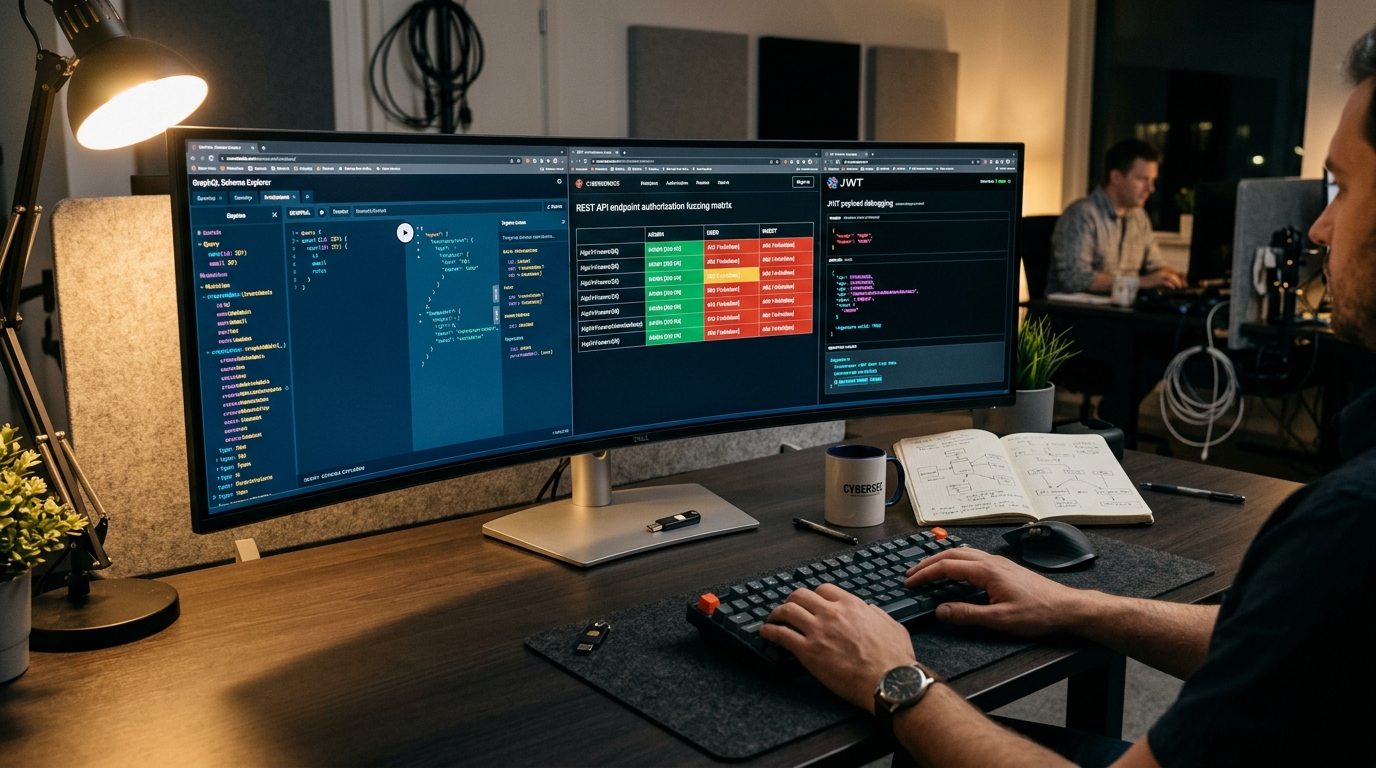
We go after the endpoints that quietly move your real data, including the ones missing from your documentation.
Explore assessment
Mobile Application Testing
We test your iOS and Android apps and the backends they talk to, including what the app leaves behind on a lost phone.
Explore assessment
Cloud Security Testing
We stress-test your half of the cloud shared-responsibility model, auditing identity, permissions, configuration and gaps between services.
Explore assessmentReady to scope your Web Application Testing?
Tell us about your hardware architecture, target deployment dates, or compliance deadlines. We will outline the exact test plan, timeline, and deliverables.