Red Teaming.
A full-scope, no-warning rehearsal of a real attack against your technology, your process and your people at the same time.
The attack surface & hardware challenge
Offensive reverse-engineering down to the physical silicon, flash extraction, and protocol buses to uncover deep architectural flaws.
The Red Teaming Challenge
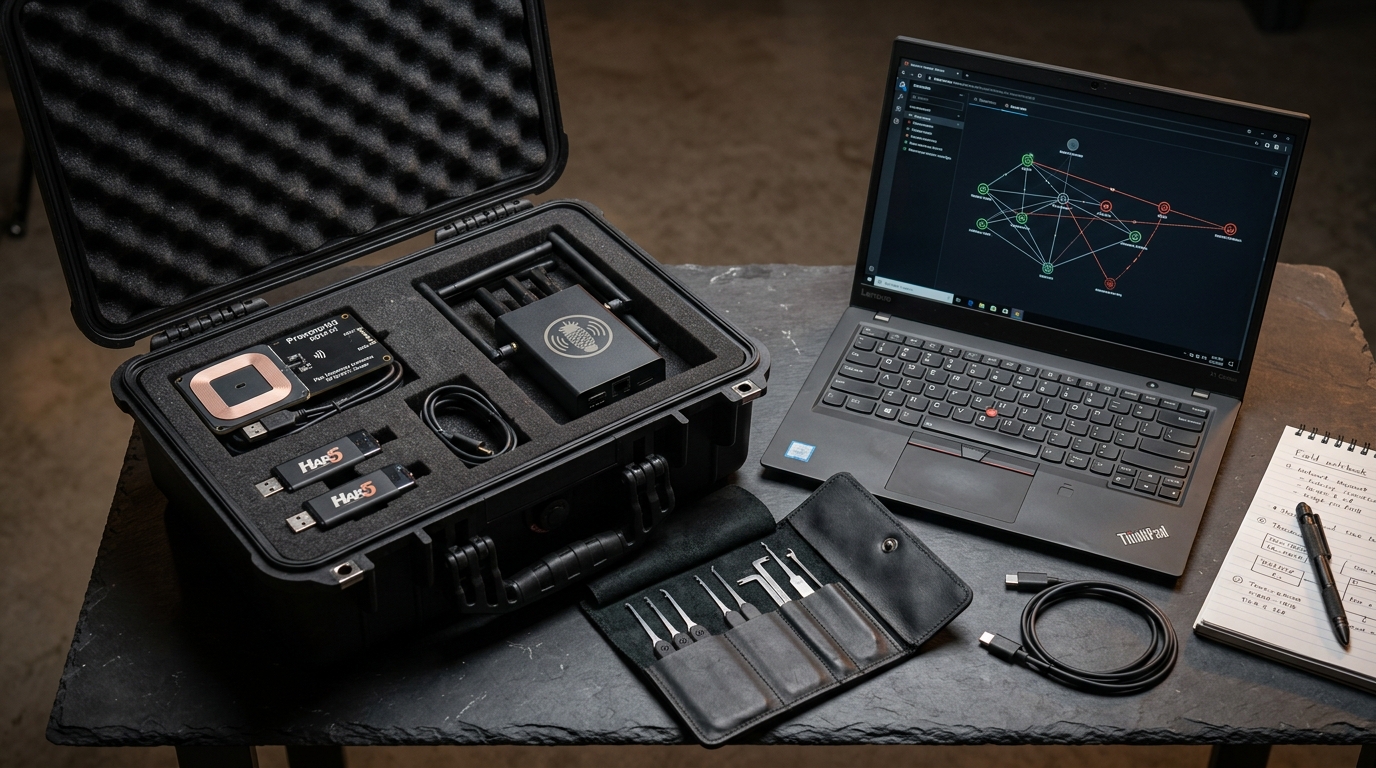
Red Teaming goes beyond traditional penetration testing by simulating real-world adversarial attacks to test your organization's ability to detect, respond to, and withstand sophisticated cyber threats. In today's threat landscape, organizations need to understand their true security posture against determined attackers. At Dellon, we understand that Red Teaming extends beyond finding vulnerabilities to test your entire security posture, evaluating technology, personnel, and operational processes together.
What the assessment covers
Exhaustive penetration testing vectors executed across hardware, firmware, interface buses, and logic layers.
Adversary Simulation
Comprehensive simulation of real-world attack scenarios using tactics, techniques, and procedures (TTPs) employed by advanced threat actors and nation-state attackers.
Social Engineering
Advanced social engineering campaigns including phishing, spear phishing, vishing, SMiShing, and physical social engineering to test human security awareness.
Physical Security Testing
On-site security assessments including physical penetration testing, tailgating, lock picking, and bypassing physical security controls.
Cyber Threat Intelligence
Integration of real-world threat intelligence to simulate attacks based on current threat actor capabilities, motivations, and targeting patterns.
How we run the engagement
Structured four-phase offensive methodology engineered to minimize engineering friction and deliver clear, actionable findings.
Planning & Scoping
Comprehensive assessment of your organization's threat landscape, critical assets, and security objectives to define realistic attack scenarios and success criteria.
Reconnaissance & Intelligence
Gathering open-source intelligence, analyzing your digital footprint, and developing attack plans based on real-world threat actor methodologies.
Execution & Persistence
Controlled execution of attack scenarios with stealth techniques, lateral movement, and persistence mechanisms to test your detection and response capabilities.
Reporting & Remediation
Comprehensive red team report with attack timeline, detection gaps, response effectiveness, and prioritized recommendations for security improvements.
Why engineering teams choose this assessment
Evidence-based vulnerability research designed to unblock compliance, protect launch timelines, and prevent post-shipment recalls.
Real-World Attack Experience
Extensive experience with actual threat actor TTPs, advanced attack techniques, and nation-state methodologies across various industries and attack surfaces.
Comprehensive Assessment
Holistic approach covering cyber attacks, social engineering, physical security, supply chain risks, and insider threats for complete security posture evaluation.
Practical Insights
Actionable insights into your organization's true security capabilities, detection gaps, and response effectiveness with realistic improvement recommendations.
Proven Track Record
Successfully conducted 100+ red team engagements across financial institutions, government agencies, and enterprise organizations with measurable security improvements.
Advanced Methodologies
Custom attack frameworks, zero-day exploit development, and sophisticated evasion techniques to test against the most advanced threats.
24/7 Support
Round-the-clock security consultation and emergency response during red team engagements. We're always available when your security posture is being tested.
Also in Adversary Simulation
Teams booking Red Teaming frequently combine it with these adjacent assessments for end-to-end assurance.
Threat Intelligence & OSINT
We look at your organisation the way an attacker researching you would, using only what is publicly available.
Explore assessment
Information Security Assessment
A structured review of your security posture, your processes and the gaps between what is written down and what actually happens.
Explore assessmentReady to scope your Red Teaming?
Tell us about your hardware architecture, target deployment dates, or compliance deadlines. We will outline the exact test plan, timeline, and deliverables.